

The block editor refuses to save. A mobile app cannot connect. Your headless front end shows nothing. When wordpress rest api returns 404 error, WordPress’s data API — the wp-json endpoints everything modern uses to talk to your site — is unreachable. The site looks fine to visitors, but anything that needs the API is dead.
The REST API depends on rewrite rules, so its 404s are usually routing problems: broken permalinks, damaged .htaccess, a security plugin blocking the endpoints, or the server missing mod_rewrite. This guide restores the API in order, from the one-click permalink resave to server-level checks. Keep FTP/hosting access handy.
Table of Contents
- Quick Checks
- Diagnosing wordpress rest api returns 404 error
- Fix 1: Resave Permalinks
- Fix 2: Fix .htaccess
- Fix 3: Deactivate Security Plugins
- Fix 4: Enable mod_rewrite
- Fix 5: Test Plain Permalinks
- Fix 6: Check the Server Firewall
- Fix 7: Enable Debugging
- What to Avoid
- Frequently Asked Questions
- Conclusion
- Helpful Official Resources
Quick Checks
Fast checks before the fixes.
- Visit
https://yoursite.com/wp-json/directly. A 404 here confirms the API routing is broken (not just one app). - Check whether the block editor can save — the editor needs the API, so its failure corroborates.
- Note when it started: after migration, after a security plugin install, after moving hosts?
- Test in Incognito to rule out browser weirdness.
- Check the site is on https consistently — mixed protocol setups confuse API routing.
Diagnosing wordpress rest api returns 404 error
| Symptom | Cause | Go to Fix |
|---|---|---|
/wp-json/ 404s, started after migration | Rewrite rules not regenerated | Fix 1 |
| 404s plus other odd routing | Damaged .htaccess | Fix 2 |
| API worked until a security plugin arrived | Plugin blocking wp-json | Fix 3 |
| Fresh server / new host, API never worked | mod_rewrite missing | Fix 4 |
| Pretty permalinks 404 but plain work | Rewrite engine problem | Fix 5, then Fix 4 |
| Intermittent API failures | Firewall rate-limiting | Fix 6 |
Fix 1: Resave Permalinks
The REST API rides on WordPress’s rewrite rules. Resaving permalinks regenerates them — the one-click fix for most API 404s.
- Go to Settings > Permalinks in wp-admin.
- Without changing anything, click “Save Changes”.
- This flushes and regenerates the rewrite rules.
- Visit
/wp-json/again — it should now show the API index JSON. - Test the block editor save and any apps.
- If you cannot reach wp-admin, flush via WP-CLI (
wp rewrite flush) if you have SSH access.
Resaving is harmless and takes seconds — it is always worth trying first for any routing weirdness. Migrations are the classic trigger: rules generated for the old server do not suit the new one. For plain 404 page errors rather than API ones, our WordPress 404 error fix guide is the sibling.
Fix 2: Fix .htaccess
If resaving did not help, the .htaccess file itself may be damaged or missing the WordPress block.
- Via FTP or file manager, back up the
.htaccessfile in your WordPress root. - Open it and confirm the WordPress block exists:
# BEGIN WordPress\n RewriteEngine On\n RewriteRule .* - [E=HTTP_AUTHORIZATION:%{HTTP:Authorization}]\n RewriteBase /\n RewriteRule ^index\\.php$ - [L]\n RewriteCond %{REQUEST_FILENAME} !-f\n RewriteCond %{REQUEST_FILENAME} !-d\n RewriteRule . /index.php [L]\n # END WordPress- If the block is missing or mangled, replace it with the above (for root installs; subdirectory installs need the path adjusted).
- Save, upload, and test
/wp-json/. - If the site breaks, restore your backup.
The !-f and !-d lines are the magic: they send non-file, non-directory requests (like /wp-json/...) to WordPress. Without them, the server looks for a literal wp-json file, finds nothing, and 404s. If the whole site shows critical errors instead, see WordPress critical error fix.
Fix 3: Deactivate Security Plugins
Security plugins love blocking wp-json — to them, API traffic looks like bot probing. One overzealous rule 404s the entire API.
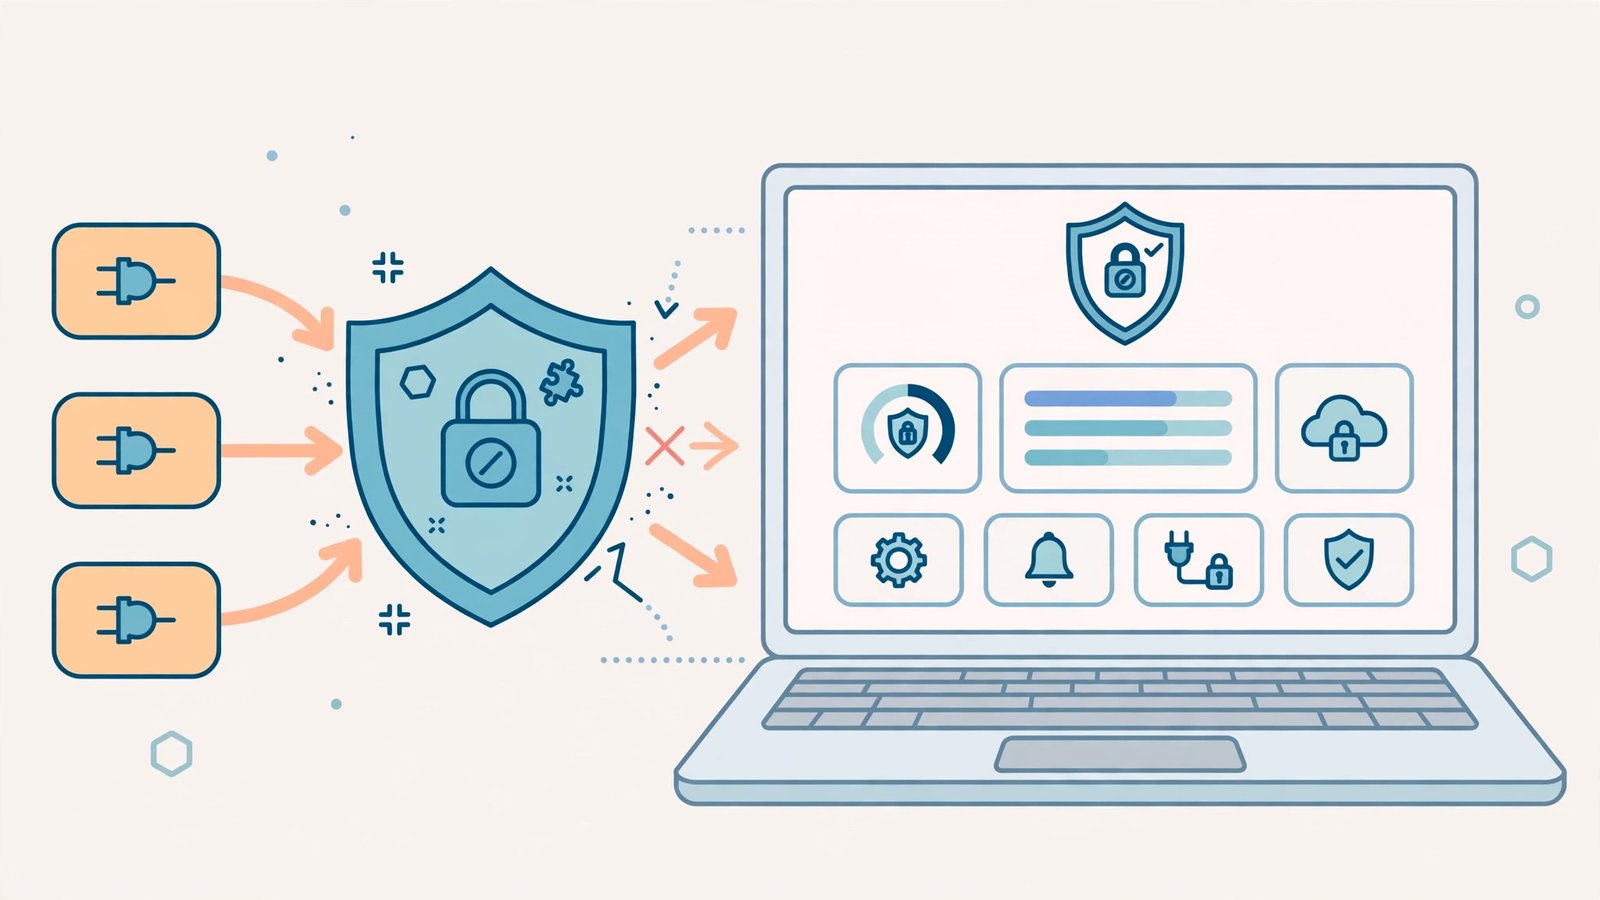
- In wp-admin > Plugins, deactivate your security plugin(s) temporarily.
- Test
/wp-json/immediately. - If the API returns, the plugin was blocking it — check its firewall/WAF settings for a “disable REST API” or bot-protection option and whitelist legitimate API use.
- Some security plugins have an explicit “Disable REST API for visitors” setting — turn it off unless you specifically need the API private.
- If wp-admin is unreachable, rename the plugin’s folder via FTP (
wp-content/plugins/) to deactivate. - Reactivate the plugin after configuring its exception.
Do not leave the security plugin off permanently — configure the exception instead. The goal is a protected site with a working API, not a choice between the two. For login-page troubles, our WordPress login page not working guide is related.
Fix 4: Enable mod_rewrite
On Apache servers, pretty permalinks — and the API — need the mod_rewrite module. Fresh servers and some hosts lack it.
- Ask your host whether mod_rewrite (Apache) is enabled. Most shared hosts have it; some VPS setups do not.
- If you control the server, enable it (e.g.
a2enmod rewriteon Ubuntu) and restart Apache. - Also confirm
AllowOverrideis set so .htaccess rules actually apply — without it, the WordPress block is ignored. - On Nginx servers there is no .htaccess: the host must include the WordPress rewrite rules in the server config. Ask them to verify.
- After the server change, resave permalinks (Fix 1) and test
/wp-json/.
This is squarely host/server territory — do not feel bad opening a ticket. “Please enable mod_rewrite and AllowOverride for my WordPress site” is a routine request they handle daily. If the site will not load at all, see WordPress website not loading.
Fix 5: Test Plain Permalinks
Switching to plain permalinks (?p=123) bypasses rewrite rules entirely. If the API works on plain but 404s on pretty, the rewrite engine is confirmed as the problem area.
- Go to Settings > Permalinks and switch to “Plain”.
- Save, then test
/wp-json/— note: with plain permalinks the API lives at/?rest_route=/. - If the API works here, rewrites are broken — return to Fixes 2 and 4 with that knowledge.
- Switch back to your pretty permalink structure afterwards and resave.
- Do not leave plain permalinks permanently unless you must — pretty URLs are better for SEO and users.
This is a diagnostic step, not a solution — but it cleanly separates “rewrite problem” from “API problem”, which focuses everything that follows.
Fix 6: Check the Server Firewall
Server firewalls and bot-protection (ModSecurity rules, Cloudflare WAF) can block or rate-limit API requests, producing intermittent 404s or 403s.
- Check whether API failures are intermittent — firewall blocks often are.
- In Cloudflare, check the Firewall > Events log for blocked
/wp-json/requests and create an exception. - Ask your host whether ModSecurity rules might block REST requests — they can whitelist the pattern.
- If you use a WAF plugin, add
/wp-json/*to its allowlist. - Test the API after each change.
Intermittent failures are the fingerprint here: works, fails, works. Consistent 404s point at rewrites (Fixes 1–4); flaky ones point at the firewall. Distinguishing them saves hours.
Fix 7: Enable Debugging
When the API 404s for no clear reason, WordPress’s debug log reveals the underlying error.
- Via FTP, open
wp-config.php. - Add (or change) these lines above the “stop editing” comment:
define('WP_DEBUG', true);\n define('WP_DEBUG_LOG', true);\n define('WP_DEBUG_DISPLAY', false);- Trigger the API 404 again, then open
wp-content/debug.logvia FTP. - Read the latest entries — they name the failing file and line.
- Fix what the log reveals (often a plugin fatal error killing the API bootstrap).
- Turn debugging off afterwards by setting the values back to false — debug logs can grow huge and may expose paths.
The debug log is the last resort that rarely fails: PHP always knows why it died; WP_DEBUG just makes it tell you. The official WordPress debugging guide (linked below) documents every option.
What to Avoid
- Do not disable the REST API “for security” unless you understand what breaks — the block editor needs it.
- Do not edit .htaccess without a backup — one typo 500s the whole site.
- Do not leave plain permalinks on permanently as a “fix” — solve the rewrite problem instead.
- Do not ignore the first console/network error — in browser DevTools, the failing request names the issue.
- Do not reinstall WordPress for an API 404 — the content and API code are fine; routing is the problem.
- Do not leave WP_DEBUG on in production — logs grow and can leak information.
Frequently Asked Questions
What is the WordPress REST API?
A built-in interface letting apps, the block editor, and external services read and manage your site’s content as data. yoursite.com/wp-json/ is its front door — it should show JSON, not a 404.
Why does the block editor need the REST API?
The editor saves and previews through API requests. A 404ing API means the editor cannot save — the “updating failed” error is the visible symptom of this invisible cause.
Will resaving permalinks break my URLs?
No — resaving regenerates the same rules. Your URLs do not change; only the internal routing table refreshes. It is one of the safest actions in WordPress.
Can a security plugin really block the whole API?
Yes — many include “disable REST API” features or WAF rules that match API traffic patterns. Whitelist legitimate use rather than disabling protection entirely.
Why does /wp-json/ work on plain permalinks but not pretty?
Because pretty permalinks need rewrite rules (Fixes 1, 2, 4) while plain ones do not. The API itself is fine — the routing to it is broken.
Can I use the REST API without pretty permalinks?
Yes. With plain permalinks, the API lives at yoursite.com/?rest_route=/ instead of /wp-json/. WordPress understands both forms. This is a useful fallback when rewrite rules are broken — and it is exactly how Fix 5 diagnoses whether the problem is routing or the API itself. Pretty permalinks are nicer, but the API does not require them.
Why do some API endpoints 404 while others work?
Endpoints are registered by WordPress core and by plugins. If a plugin that registered custom endpoints is deactivated or broken, its endpoints 404 while core endpoints keep working. Check the failing endpoint’s prefix — /wp-json/wp/v2/ is core, anything else belongs to a plugin. Revisit Fix 3’s plugin conflict test with that plugin in mind.
Is the REST API a security risk I should just disable?
Disabling it breaks the block editor, the mobile apps, and many plugins — a heavy price. The API only exposes what WordPress already makes public; write operations need authentication. Instead of disabling it, keep WordPress updated, use strong passwords, and let your security plugin protect the endpoints rather than blocking them outright.
Why does the API work for logged-in users but 404 for visitors?
A security plugin or server rule is likely blocking unauthenticated API requests specifically — many “harden WordPress” guides recommend exactly this. Check the security plugin’s REST API settings for a “require authentication” option. If your site needs public API access (headless front end, public embeds), that option must stay off.
Conclusion
When wordpress rest api returns 404 error, the API code is innocent — the routing is guilty. Resave permalinks, repair .htaccess, calm the security plugins, confirm mod_rewrite, and let WP_DEBUG have the last word. The /wp-json/ index loading as JSON is the green light: the editor saves, the apps connect, and the headless front end breathes again.